Constrained Language Mode, App Control, and how few orgs actually roll this out
Matt Nelson posted a Constrained Language Mode circumvention that works in App Control environments. The research is useful. The more interesting number is how few environments it actually applies to and why that gap exists.
Matt Nelson posted a Constrained Language Mode circumvention that works in an App Control for Business environment. He reported it and noted it was treated as by design.

Jimmy’s first instinct was to check whether this was a 2017 post coming back around. This has been around.
The research is useful. What I keep coming back to is how few environments it actually applies to.
CLM is not a standalone switch. PowerShell moves into Constrained Language when App Control is on with user-mode code integrity and script enforcement. Microsoft’s docs are a little messy across versions, but the practical bar is the same. If the policy is only sitting in audit and nothing is really being enforced, most sessions stay in Full Language. That is still what the average estate is running. See about_Language_Modes and How App Control works with PowerShell.
There is no good data source for the US. The cleanest official numbers we have are from Australia, and those agencies are required to do this. ASD’s Commonwealth Cyber Security Posture in 2025 covered federal entities with a 94 percent survey response:
- Application control at Essential Eight ML2+: 48%
- Full Essential Eight ML2 across all eight strategies: 22%
Non-corporate Commonwealth entities have been required to hit ML2 since July 2022. Even with that requirement, fewer than half clear application control. The United States does not have an equivalent commercial mandate. CISA treats allowlisting as recommended practice. Intune App Control for Business only got group-scoped targeting at GA in August 2025.
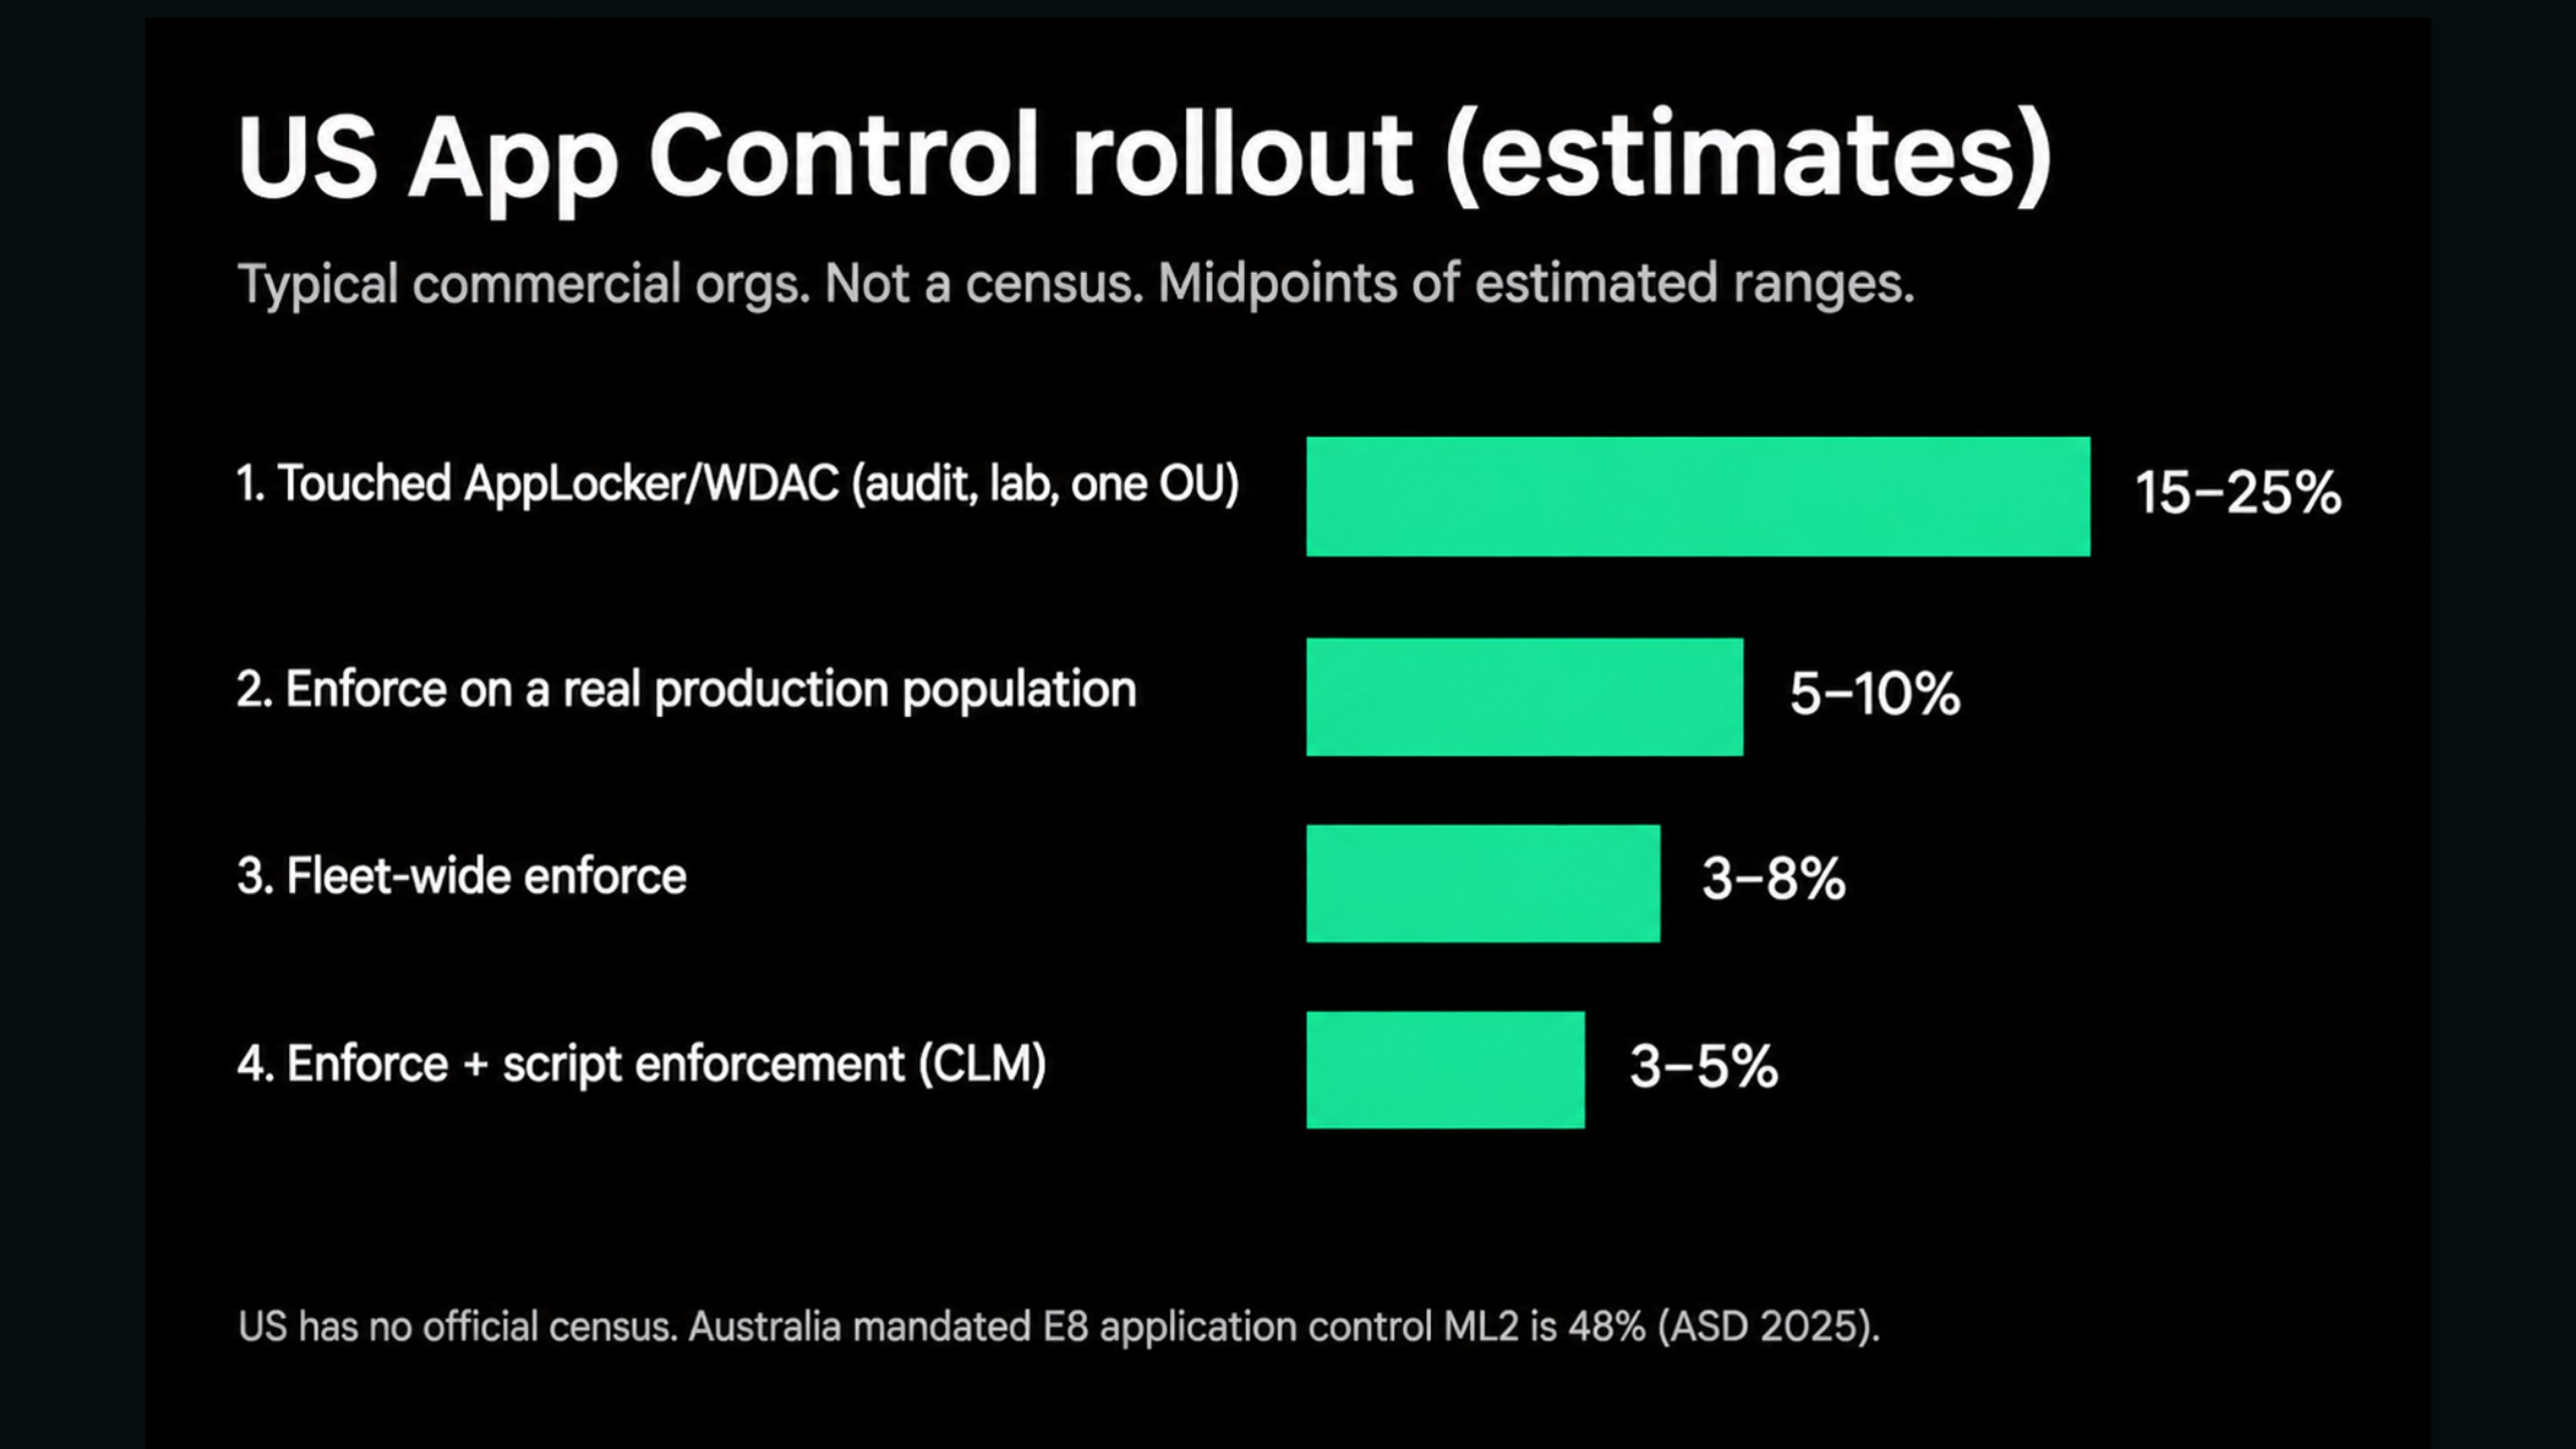
Given that, this is how I would size a typical US org:
- Ever stood up AppLocker or WDAC in audit, a lab, or one OU: 15% to 25%
- Enforce mode on a real production population: about 5% to 10%
- Fleet-wide enforce: about 3% to 8%
- Enforce plus script enforcement, which is the setup that actually puts PowerShell in CLM: about 3% to 5%
So the technique matters for the small set of shops that actually shipped the control. For everyone else there is nothing to circumvent.
That really is the part that bugs me more than the vulnerability itself. Most companies do not roll this out because it is hard to deploy. One unsigned script that the business still needs can throw the whole process into a spin.
If you are in that 5%, signed policy and script enforcement still matter. If you are not, this is a preview of work that has not started yet.
I would like to hear where other people would put the US enforce-mode number.
Not sure what breaks when you turn on script enforcement? CLM Forge shows you before you find out in production, free and open source. Already in enforce mode? MagicSword keeps the policy current. Free for up to 100 endpoints.
Sources
Matt Nelson (@enigma0x3), CLM / App Control post and gist note (reported, treated as by design): https://x.com/enigma0x3/status/2100628652664787319
Jimmy (@bohops) on that thread: https://x.com/bohops/status/2100757635414859989
ASD, The Commonwealth Cyber Security Posture in 2025 (application control 48% at ML2+; overall E8 ML2 22%): https://www.cyber.gov.au/about-us/view-all-content/reports-and-statistics/the-commonwealth-cyber-security-posture-in-2025
Microsoft Learn, Understand App Control script enforcement (interactive PowerShell / UMCI / audit nuance): https://learn.microsoft.com/en-us/windows/security/application-security/application-control/app-control-for-business/design/script-enforcement
Microsoft Learn, How App Control for Business works with PowerShell: https://learn.microsoft.com/en-us/powershell/scripting/security/app-control/how-app-control-works
Microsoft Learn, about_Language_Modes: https://learn.microsoft.com/en-us/powershell/module/microsoft.powershell.core/about/about_language_modes
Microsoft Learn, App Control for Business overview: https://learn.microsoft.com/en-us/windows/security/application-security/application-control/app-control-for-business/appcontrol
Microsoft Intune, What’s New in Microsoft Intune: August 2025 (App Control for Business GA and group targeting): https://techcommunity.microsoft.com/blog/microsoftintuneblog/what%E2%80%99s-new-in-microsoft-intune-august-2025/4445612

Written by
Jose Hernandez
Threat Researcher
Jose Enrique Hernandez formed and served as the Director of Threat Research at Splunk. Jose is known for creating several security-related projects, including: Splunk Attack Range, Splunk Security Content, Git-Wild-Hunt, Melting-Cobalt, lolrmm.io and loldrivers.io. He also works as a maintainer to security industry critical repositories such as Atomic Red Team and lolbas-project.github.io.


